AI Infrastructure
Production AI Shifts From Prompt Engineering to Platform Engineering
Major themes from QCon AI Boston 2026 reveal that deploying AI agents safely at scale requires rethinking infrastructure, trust, and organizational adoption strategies.

InfoQ
The QCon AI Boston 2026 conference revealed a fundamental shift in how organizations approach AI in production: the focus has moved away from crafting better prompts and toward building robust systems infrastructure.
The emphasis isn't on raw model speed anymore. OpenAI's Martin Spier opened the event by highlighting how much hidden work happens before inference—managing context windows, trimming inputs for both helpfulness and performance, and orchestrating the entire flow. Modern AI products still have significant engineering work to do even when the underlying models are fast.
From Single Apps to Shared Platforms#
A dominant theme across sessions was teams graduating from one-off, single-purpose applications toward shared infrastructure layers. Context management, tool access, identity systems, and state handling are increasingly becoming central platform concerns rather than application-level problems.
This includes emerging architectural ideas:
- Context engineering as core infrastructure, not a feature
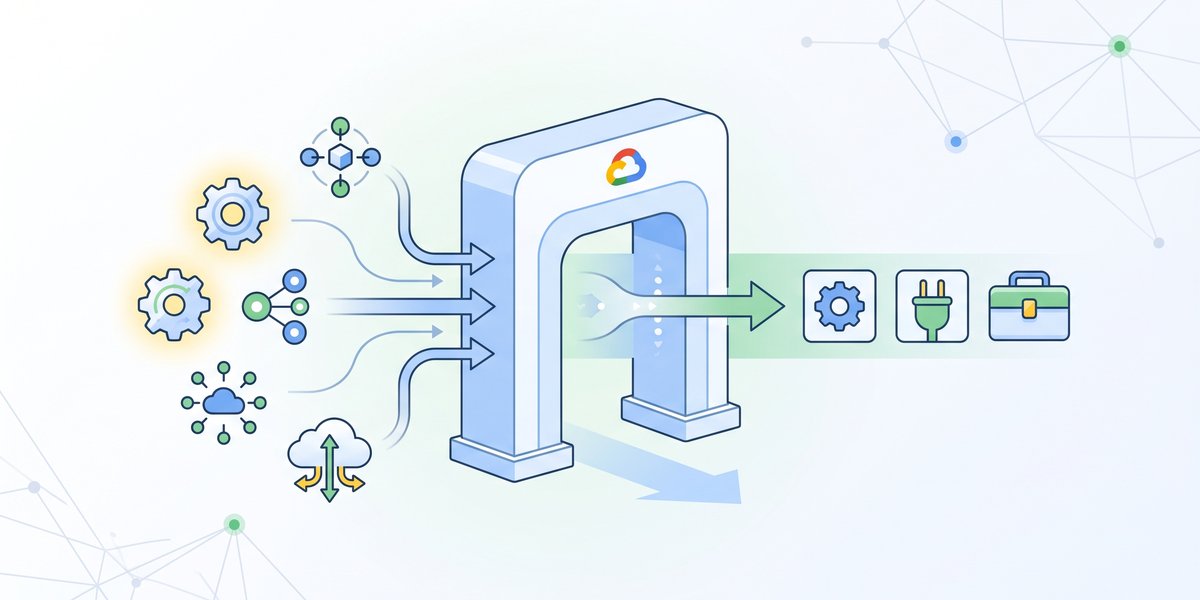
- MCP gateways for standardized tool access
- Semantic tool catalogs for discoverability and safety
- Data layers designed specifically for agent access patterns
These building blocks now need formal ownership, clear contracts, and governance—hallmarks of platform-level components.
Trust Through Execution Harnesses#
A second critical shift involves moving security beyond prompt-level guardrails. As agents gain access to real tools and data, instructions in a prompt can no longer be the primary defense. Instead, organizations need what speakers called an "agent harness"—a protective layer that wraps the model itself.
This harness must handle:
- Clear state ownership and ordered mutations
- Approval boundaries for sensitive operations
- Audit trails proving what was executed and by whom
- Privilege controls determining which tools each agent can invoke
The core problem changes from "Did the agent give a good answer?" to "Can the system prove what action was taken, which component took it, and under which constraints?"