AI Infrastructure
HCP Terraform Reimagines Infrastructure Control for AI-Driven Automation
HashiCorp argues that as coding agents handle infrastructure configuration at machine speed, the focus must shift from writing code to governing and safely executing it through a centralized control plane.

InfoQ
The rapid proliferation of AI coding agents is reshaping how infrastructure teams think about automation. Rather than having humans laboriously craft and review infrastructure configurations, AI can now generate and apply changes at machine speed. This acceleration, however, introduces a new problem: how to ensure that autonomous agents operate within organizational guardrails rather than gaining unfettered access to critical systems.
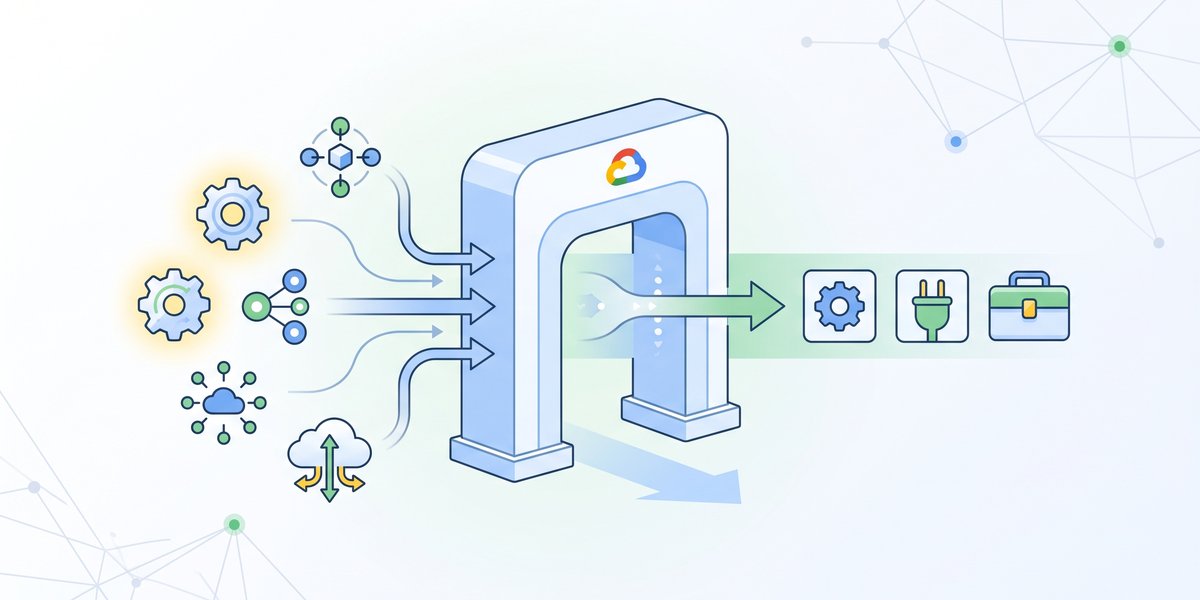
HashiCorp is positioning HCP Terraform as a governance layer purpose-built for this AI-first world. The company argues that infrastructure-as-code tools must evolve from passive execution engines into active control planes—systems that permit agent autonomy while simultaneously enforcing policy, identity restrictions, and audit trails.
The Shift from Review to Governance#
Traditional infrastructure workflows rely on human judgment: an engineer carefully examines a proposed change before deployment. AI agents operate differently. They can generate configuration, execute a plan, observe outcomes, adjust their approach, and iterate—all without pausing for human approval. This speed creates a fundamental tension: how do you gain the efficiency of continuous machine-driven iteration without losing visibility and safety?
HashiCorp's answer sidesteps manual oversight. Rather than requiring humans to review every agent action, the platform enforces a consistent set of automated controls across all infrastructure changes, whether initiated by people or machines. The distinction matters: agents propose; the control plane approves.
Layered Controls for Agent Operations#
HCP Terraform introduces multiple defensive mechanisms:
- Approved modules and standards give agents authoritative context for infrastructure decisions
- Policy-as-code and run tasks automatically evaluate proposed changes against organizational rules
- Project-scoped identities restrict which resources an agent can access
- Isolated projects and workspaces limit the scope of any single mistake or compromise
- Run history creates permanent records of plans, policy decisions, and execution details
Critically, agents cannot approve their own work, weaken existing policies, or acquire broad cloud credentials. This design principle—the agent proposes, the control plane decides—prevents machines from circumventing governance entirely.